
Learn how M-26-14 and CISA’s new Logging Reference Architecture shape federal logging and continuous monitoring requirements.
Join Datadog public sector experts for a practical look at the new federal logging guidance, including Continuous Event Monitoring (CEM) and Threat Hunting, Investigation, Response, and Forensics (THIRF) objectives.
In this session, you’ll learn how you can:
- Assess logging visibility: Understand the coverage needed across cloud, hybrid, on-premises, OT, and IoT environments
- Support continuous monitoring: Explore the logging and observability capabilities needed to advance CEM objectives
- Strengthen log retention: Understand requirements for collecting, searching, retaining, and accessing critical log data
- Improve threat detection and investigation: See how unified observability and security data can provide greater context for THIRF objectives
- Accelerate response with AI: Explore how AI and automation can surface issues faster and reduce analyst toil
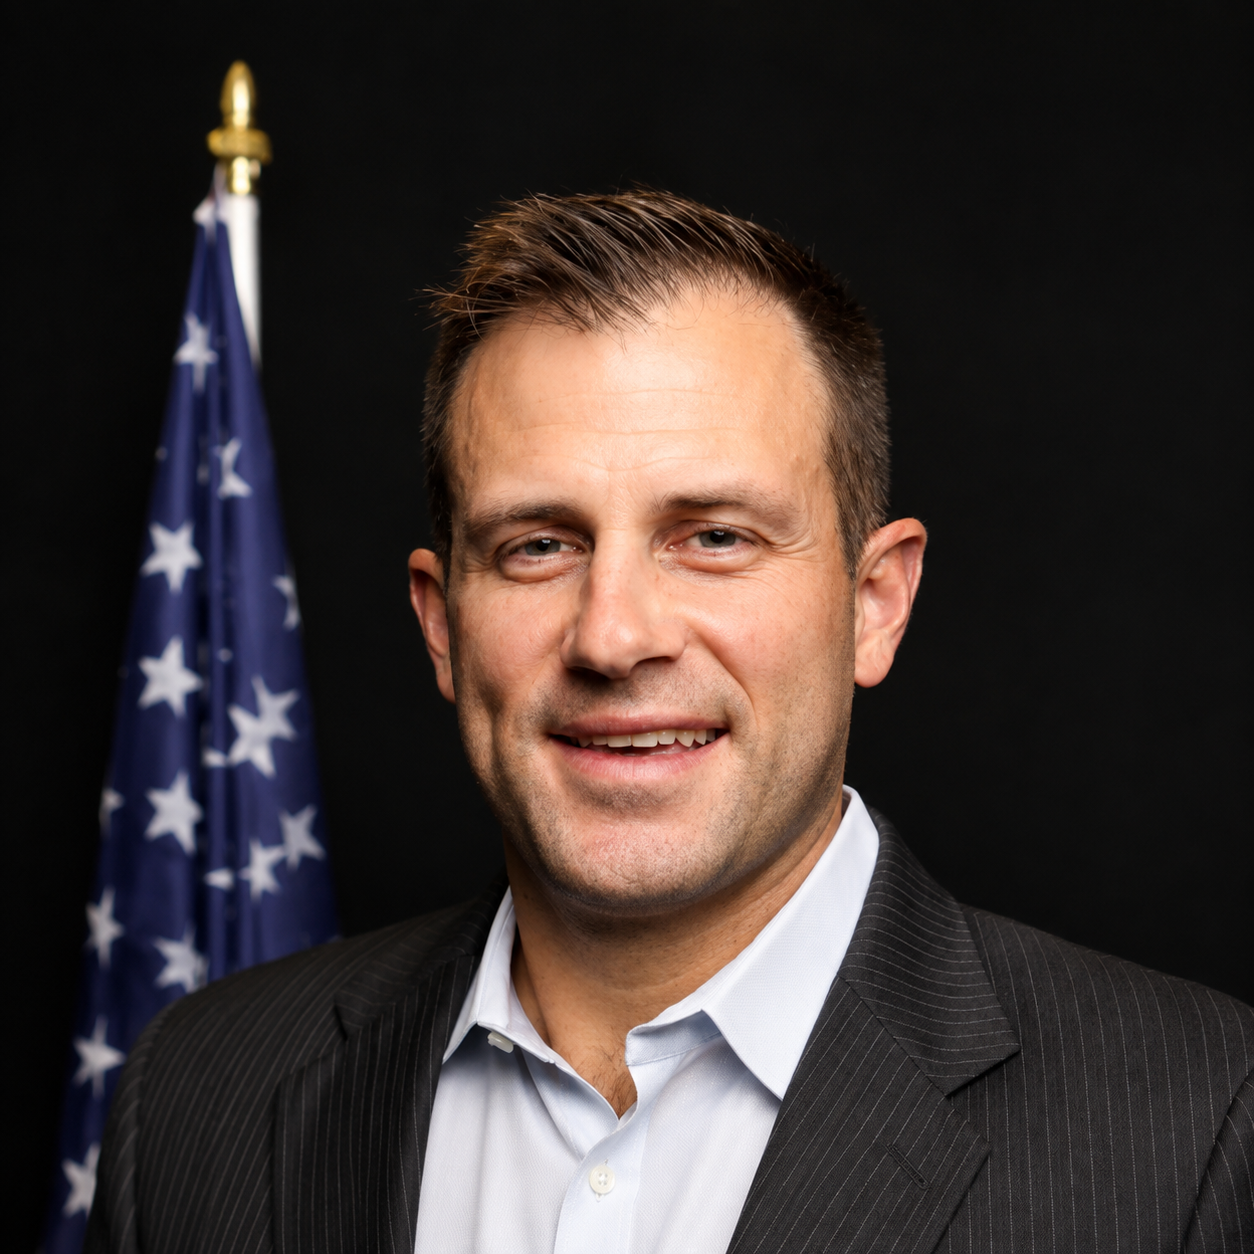
Jimmy Cesario
Federal Director, Datadog
David Pope
Sales Engineering Manager, Datadog