
How confident are you that your digital assets are safe? Do you have exposed vulnerabilities you aren’t aware of? Penetration Testing (Pen Testing) offers a proactive approach to answering these questions, helping you to identify and mitigate these vulnerabilities before malicious actors can exploit them.
Why Conduct Pen Testing?
- Regulatory Compliance:
- Comprehensive Cybersecurity Strategy:
- Establishing a Security Baseline:
- Insurance and Industry Requirements:
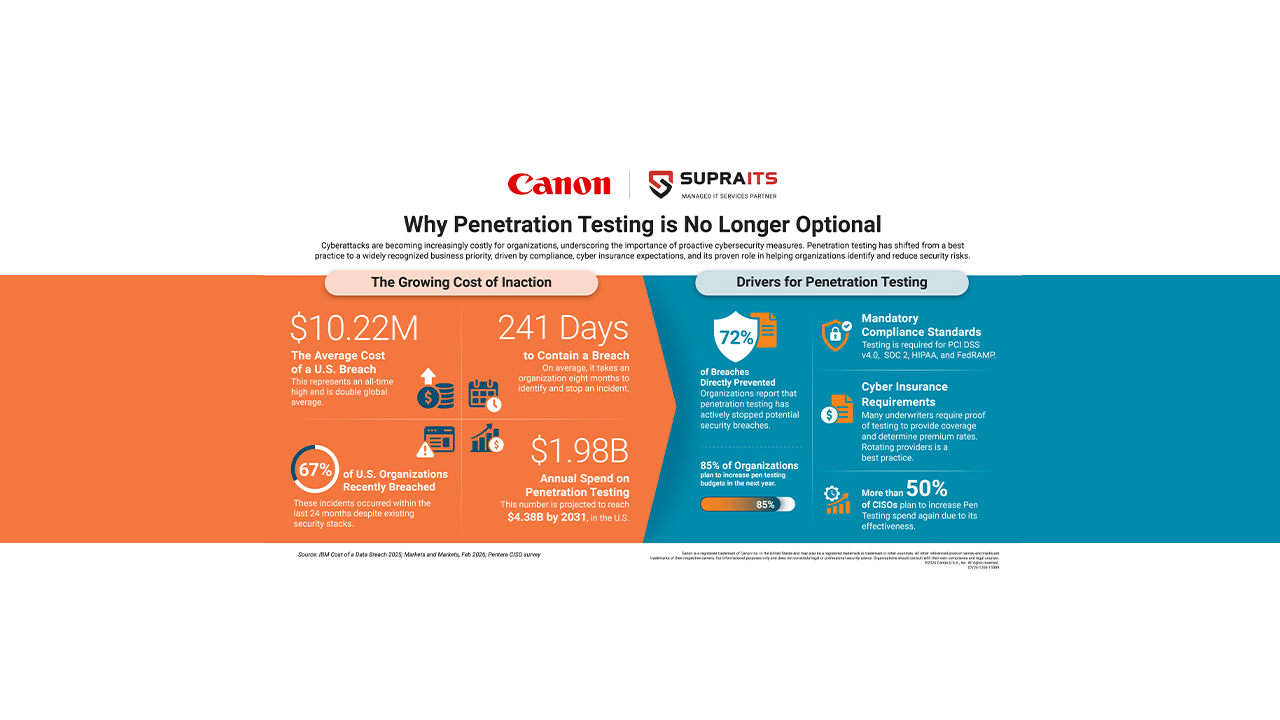
Many industries mandate regular penetration testing to adhere to standards such as HIPAA, PCI DSS, SOC, and ISO 27001. Ensuring compliance helps you avoid legal repercussions and shows your commitment to data security.
Integrating pen testing into your cybersecurity framework helps detect and address vulnerabilities, enhancing overall defense mechanisms.
Conducting an initial pen test sets a benchmark for your organization’s security posture, making it easy to measure improvements over time.
Many insurance policies and industry regulations require regular penetration testing to validate the effectiveness of security controls.